Virtual CISO
Fractional CISO and security program leadership
Fractional CISO — roadmap, board packs, vendor review, and incident command.
A senior security executive embedded 2–3 days a week: 12-month roadmap, risk register, vendor reviews, board reporting, and incident command — backed by the Cynarks specialist bench for VAPT, SOC, and compliance when you need depth.
- Madhapur, Ayyappa Society, Hyderabad
- Manual finding validation
- Free critical/high retest
- View sample reports
- OSCP
- CEH
- CISSP
- CISA
What vCISO covers
A Virtual CISO is a senior security executive who works with your organization part-time: building the security roadmap, owning risk decisions, managing compliance programs, briefing your board and standing beside you during incidents. You get someone who has run security programs before — with the scars and the playbooks — embedded in your leadership rhythm two to three days a week, backed by the full Cynarks bench of specialists.
When teams engage us
Startups and mid-market companies face enterprise-grade threats with no enterprise-grade leadership. Security decisions get made ad hoc — by engineers, sales commitments or fear. A vCISO installs calm, repeatable governance: a risk-ranked roadmap, a budget that makes sense, vendors that get managed, a board that's informed and an incident plan that's rehearsed. And unlike a full-time hire, you get a bench of specialists behind your executive from day one.
Executive presence
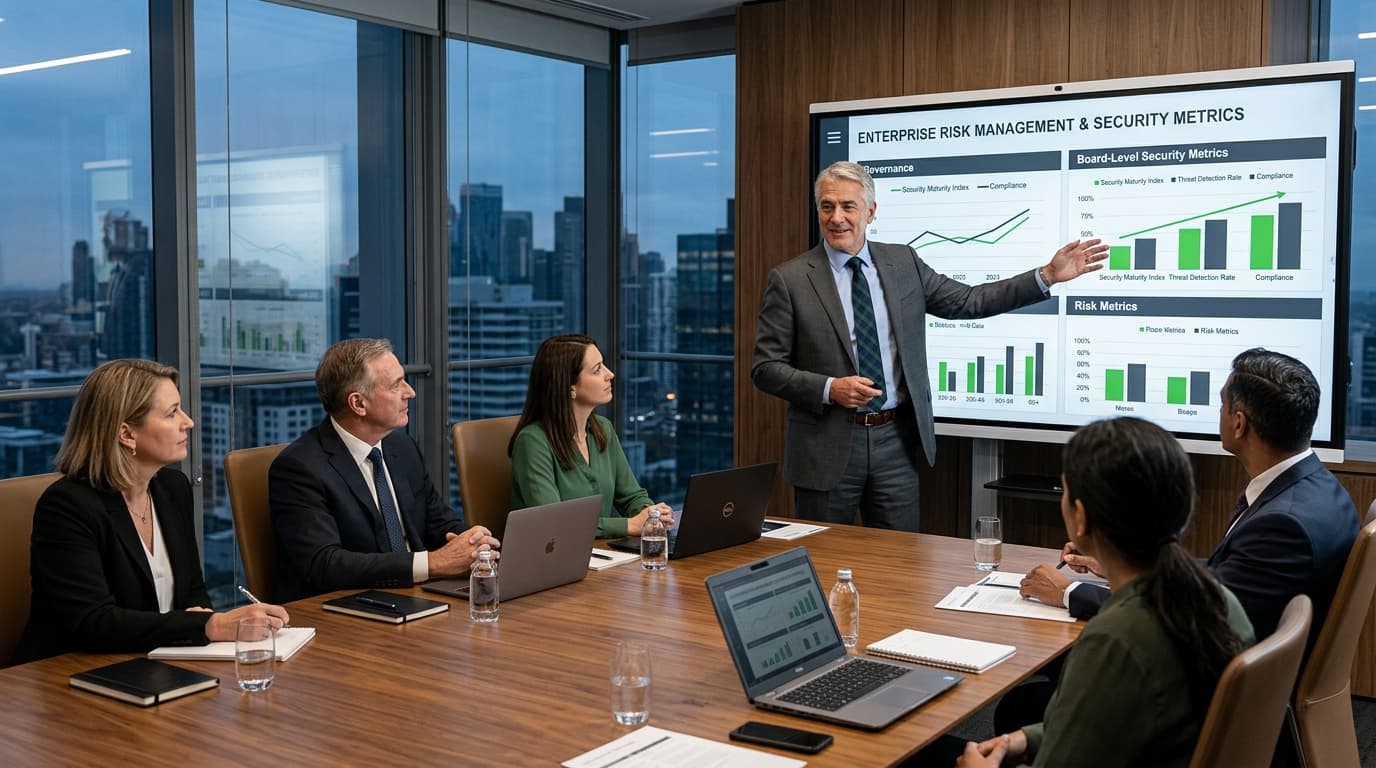
Board-ready reporting, risk language and credible leadership your stakeholders trust.
Strategy to execution
Not just advice — we drive the roadmap with your team, quarter by quarter.
Vendor-neutral
We help you buy right: tool selection, contract review and spend optimization.
Crisis-tested
Incident command experience on call — when it hits the fan, you have steady leadership.
Governance on a weekly rhythm — not ad-hoc advice.
Your vCISO owns the security roadmap, risk register, vendor reviews, and board packs, and sits in leadership meetings. When you need a pentest, SOC build-out, or ISO readiness sprint, the Cynarks bench executes under the same program.
Audit, roadmap, govern, report, review.
Five phases · 2–3 days/week · quarterly rhythm · each phase ends with named outputs you can hold us to.
NIST CSF 2.0 · ISO 27001 · FAIR risk quantification
Security strategy audit
A structured review of posture, risk appetite, regulatory exposure, team and budget reality — plus stakeholder interviews so the strategy fits how your business actually runs.
- Posture assessment
- Risk & gap summary
- Stakeholder interview notes
12-month roadmap
A risk-ranked security roadmap with budget model, owners and board-approved success metrics — sequenced against your product and compliance milestones.
- 12-month roadmap
- Budget model
- KPI definitions
Policy & vendor governance
Policy lifecycle, vendor security reviews, contract clauses and continuous third-party monitoring — governance that runs on rhythm, not reminders.
- Policy suite oversight
- Vendor review register
- Contract clause library
Board & customer reporting
Board packs that translate security into business language: KPIs, risk heat maps and progress against roadmap — plus security-questionnaire support for enterprise deals.
- Monthly board pack
- Risk heat map
- Customer questionnaire responses
Continuous advisory
Quarterly strategy reviews, incident-readiness drills, hiring input and M&A/launch support — leadership that flexes when circumstances do.
- Quarterly review deck
- Incident readiness drill
- Roadmap adjustment log
What we test and harden
Flaw classes and disciplines we prioritize on every vciso engagement.
Risk management
A risk register with owners, treatments and review rhythm — decisions documented, not vibes.
Vendor & third-party risk
Vendor assessment, contract clauses and continuous monitoring proportionate to the data each supplier touches.
Board reporting
KPIs and heat maps in business language — security your board can govern, not just fund.
Incident readiness
Response plan, command structure and an annual tabletop, so the first rehearsal is not a real breach.
Compliance strategy
Framework selection, certification calendar and auditor management aligned to sales needs, not panic.
Security budgeting
Spend justified by risk reduction — and honest advice on what not to buy yet.
Team & hiring
Org design, hiring plans and mentoring for your first security hires.
Security culture
Making security a product value your engineers own, not a department they route around.
Tools we use on this work

What you receive
Named artifacts you can open, share with auditors, and hand to engineering — not vague promises.
12-month security roadmap
Risk-ranked initiatives with budget, owners and success metrics — a document you own.
Monthly board pack
KPIs, risk posture and progress written for directors, not engineers.
Risk register & quantified exposure
Risks assessed, treated and reviewed on a rhythm, with FAIR-style quantification where it helps.
Incident response plan & tabletop
A rehearsed command structure with roles, contacts and regulator-aware comms templates.
Vendor security program
Assessment questionnaires, contract clauses and a monitoring register for your third parties.
Quarterly strategy reviews
Roadmap adjustments, budget checkpoints and readiness drills each quarter.
What we typically confirm
Flaw classes we most often validate on this engagement type — so scope conversations stay realistic.
Security decisions made ad hoc by engineering, sales or whoever shouts loudest
No risk register — or one written for an audit and never revisited
Critical vendors onboarded without any security assessment
Incident response exists as a document nobody has rehearsed
Security spend driven by fear — tools bought without a roadmap
Board informed about security only when something breaks
Compliance started and abandoned — a half-built ISMS with no owner
Customer security questionnaires answered inconsistently by different engineers
What we need from you
A short checklist so kickoff is not delayed. Most items take under an hour — and everything shared is covered by NDA from the first call.
An executive sponsor and an agreed meeting rhythm with leadership
Access to current policies, contracts, tooling and previous assessments
A board or investor reporting cadence we can plug into
A named coordinator for scheduling and document collection
Honesty about budget reality — the roadmap must fit your resources
Willingness to assign owners to roadmap initiatives
vCISO FAQ
Typically 2–3 days per week during the first quarter (build mode), settling to 1–2 days weekly for steady-state governance. Crunch periods — incidents, audits, M&A — flex up as needed.
Services often paired with this
Compliance & Governance
ISO 27001, SOC 2, PCI DSS, and India DPDP — gap analysis, ISMS build, and internal audit.
Learn moreManaged SOC
24/7 Hyderabad SOC on your SIEM, EDR, and cloud logs — human triage, hunting, and escalation SLAs.
Learn moreSecurity Training
Practitioner-led labs — phishing simulation, secure coding, SOC drills, executive tabletops.
Learn morePlanning a VAPT, red team, or cloud review?
Talk to a Cynarks engineer in Hyderabad. We map in-scope apps and networks, propose a realistic test window, and outline deliverables — so you know exactly what the engagement covers before you commit.
Madhapur · +91 73373 81478 · security@cynarks.com