Red Team Operations
Full-scope red team and adversary emulation
Objective-driven adversary emulation that measures detection and response.
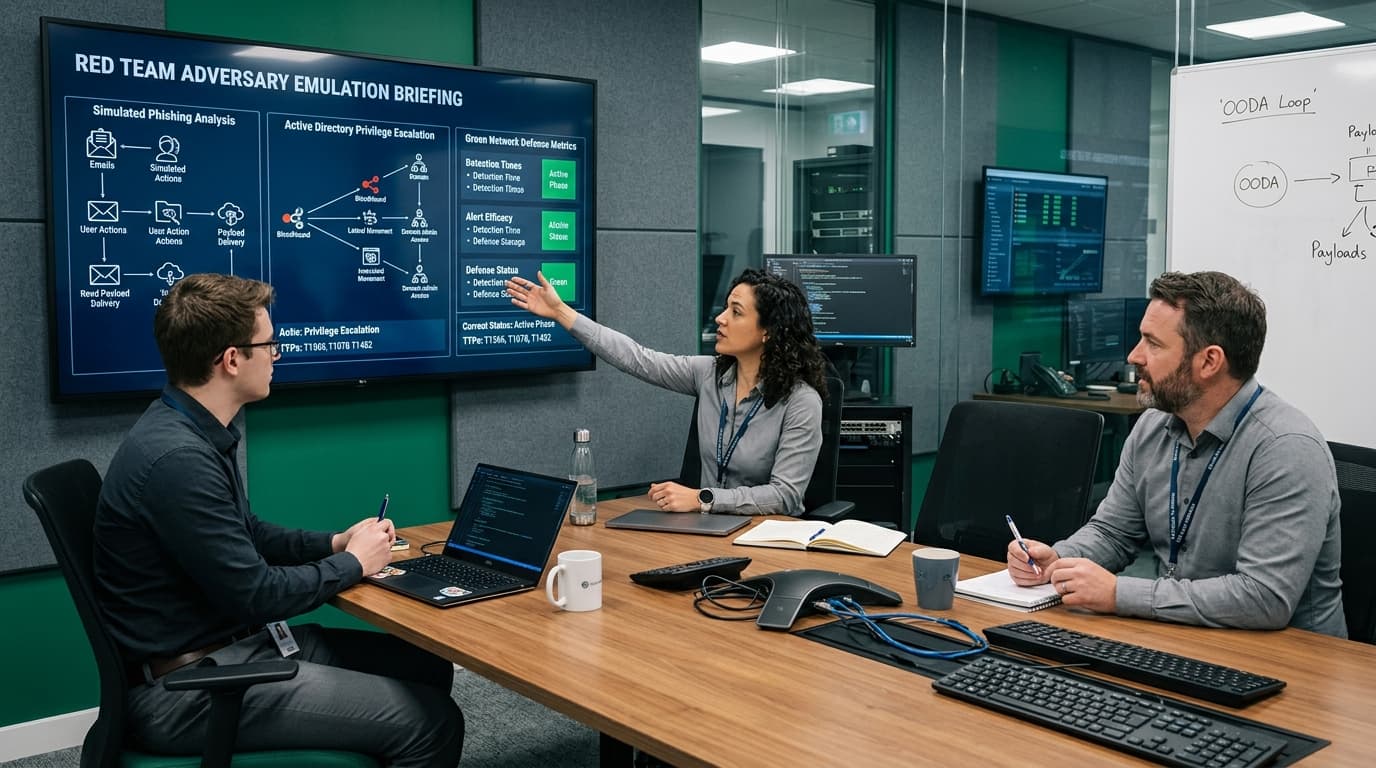
Multi-week red team operations pursue defined objectives — access payment data, prove lateral movement, test phishing resilience — using MITRE ATT&CK-mapped tradecraft under a white-cell safety protocol. The output is an attack narrative plus a detection-gap backlog for your SOC.
- Madhapur, Ayyappa Society, Hyderabad
- Manual finding validation
- Free critical/high retest
- View sample reports
- OSCP
- CEH
- CISSP
- CISA
What Red Team covers
A red team operation emulates a specific threat actor — financially motivated, nation-state or internal threat — pursuing defined objectives like 'access the payment database' or 'demonstrate exfiltration of customer PII'. Operating under strict rules of engagement and a white-cell safety protocol, we use the same TTPs as real adversaries: initial access brokers' tradecraft, C2 frameworks, credential theft and sophisticated evasion.
When teams engage us
Pentests answer 'what can they reach?' Red teams answer 'would we even know?' The metric of a red team isn't vulnerabilities found — it's detections missed. Every objective achieved without triggering an alert is a documented gap in your detection & response capability, feeding directly into SOC tuning, tabletop exercises and security investment decisions with evidence your board can't ignore.
Objective-driven
Real goals, not vulnerability quotas — measures detection & response, not just patch status.
Full-spectrum TTPs
OSINT, phishing, physical entry, hardware implants and custom C2 — scoped to your threat model.
Blue team uplift
Purple-team debriefs turn every missed detection into a concrete detection rule.
Board-grade narrative
Attack narrative report that makes risk tangible for executives and the board.
Pentests list flaws. Red teams test whether you notice.
We pursue agreed objectives with phishing, credential abuse, and lateral movement under signed rules of engagement — then replay every technique against your SIEM and EDR so missed detections become concrete Sigma rules and telemetry fixes.
Threat model, access, move, achieve, debrief.
Six phases · 3–6 weeks · objective-based · each phase ends with named outputs you can hold us to.
MITRE ATT&CK · Cyber Kill Chain · TIBER-EU · PTES
Threat modeling & authorization
We define the adversary profile, objectives and rules of engagement with your stakeholders — including white-cell protocol, abort criteria and emergency contacts. Assumptions documented, blast radius agreed.
- Threat-intelligence profile
- Rules of engagement
- Abort & safety criteria
Reconnaissance & staging
Deep OSINT on your people and attack surface, infrastructure setup, payload development and cover-traffic planning — the unglamorous work that makes operations realistic.
- Attack-surface intelligence
- Staged infrastructure
- Operation plan
Initial access
Phishing, vishing, exposed-asset compromise or physical entry — per the approved threat model. Every access path is logged for later detection analysis.
- Initial-access record
- Phish campaign metrics
- Entry evidence
Post-exploitation & lateral movement
Under white-cell watch, we escalate privileges, move laterally and map Active Directory attack paths — stopping short of anything that would harm availability.
- Lateral-movement map
- Credential-access log
- Privilege-escalation evidence
Objective execution
We pursue the agreed objectives — demonstrate data access, prove impact, document exfiltration paths without exfiltrating real data. Every step is timestamped for detection replay.
- Objective achievement record
- Impact demonstration
- Timestamped action log
Purple-team debrief & report
The full attack narrative — then joint sessions with your SOC replaying each technique against your telemetry: what fired, what didn't, and the rules to close each gap.
- Attack narrative report
- Detection gap register
- Prioritized detection backlog
What we test and harden
Flaw classes and disciplines we prioritize on every red team engagement.
Initial access vectors
Phishing, credential-stuffing, exposed perimeter and vendor paths — tested against how your organization would actually be breached.
Active Directory attack paths
Kerberoasting, ACL abuse, delegation misconfigurations and tiering violations mapped with BloodHound-style analysis.
Defense evasion
EDR-aware execution, living-off-the-land binaries, log evasion and C2 cover traffic that mirror real adversary tradecraft.
Persistence & staging
How an intruder would survive reboots and blue-team cleanup — and whether your monitoring would notice.
Credential access
The techniques attackers use to harvest credentials — and what your controls would actually stop.
Social engineering
Phishing, vishing and pretexting measured as human-layer metrics: click, report and response rates by team.
Detection gaps
Every red action replayed against your SIEM and EDR telemetry to separate what fired from what should have.
Response readiness
How long identification and escalation actually took during the operation — measured, not assumed.
Tools we use on this work

What you receive
Named artifacts you can open, share with auditors, and hand to engineering — not vague promises.
Attack narrative report
The full story of the operation — objectives, paths, evidence and impact — written for executives and engineers.
Detection gap register
Every technique that went undetected, ranked by risk, mapped to MITRE ATT&CK.
Detection engineering backlog
Sigma rules and telemetry fixes for each gap, prioritized and ready to implement.
Purple-team workshop
Joint sessions with your SOC replaying the operation against live telemetry.
Response metrics
Measured time-to-detect and time-to-respond for each phase of the operation.
Re-test of critical gaps
After remediation, we validate the fixes that mattered at no additional cost.
What we typically confirm
Flaw classes we most often validate on this engagement type — so scope conversations stay realistic.
Phishing campaigns achieving initial access without triggering any alert
Active Directory attack paths from standard user to domain admin in a few hops
EDR telemetry incomplete — key servers or cloud workloads unprotected
Privileged accounts used for daily work, exposing credentials to workstations
Security alerts generated during the operation reviewed hours or days later
No documented process to escalate a suspicious-activity report into action
Lateral movement across flat network segments with no segmentation alerts
Dormant accounts and stale credentials that made persistence trivial
What we need from you
A short checklist so kickoff is not delayed. Most items take under an hour — and everything shared is covered by NDA from the first call.
Signed rules of engagement with a named executive sponsor
Emergency contacts reachable 24/7 during the operation window
Written abort criteria and a protected-systems list
Explicit authorization for social engineering and/or physical testing (if in scope)
A commitment that your SOC will not be pre-briefed (for blind operations)
A white-cell coordination window for post-operation evidence sharing
Red Team FAQ
Yes — operations run under a white-cell protocol with hard abort criteria, protected scopes and 24/7 emergency contact. Actions that could impact availability are simulated, not executed, and anything ambiguous goes to the white cell first.
Services often paired with this
Penetration Testing
Manual VAPT across web, API, mobile, and network — PoCs, CVSS scores, and free critical/high retests.
Learn moreManaged SOC
24/7 Hyderabad SOC on your SIEM, EDR, and cloud logs — human triage, hunting, and escalation SLAs.
Learn moreApplication Security
Threat modeling, secure code review, and CI/CD gates that catch flaws before production.
Learn morePlanning a VAPT, red team, or cloud review?
Talk to a Cynarks engineer in Hyderabad. We map in-scope apps and networks, propose a realistic test window, and outline deliverables — so you know exactly what the engagement covers before you commit.
Madhapur · +91 73373 81478 · security@cynarks.com